On the Mac - FDA
The procedure to enable FDA is slightly different for different macOS versions. The following steps describe how to enable FDA on endpoints running macOS 11 (Big Sur) and macOS 12 (Monterey), and then for endpoints running macOS 13 (Ventura) through macOS 26 (Tahoe).
macOS 11 (Big Sur) and macOS 12 (Monterey)
-
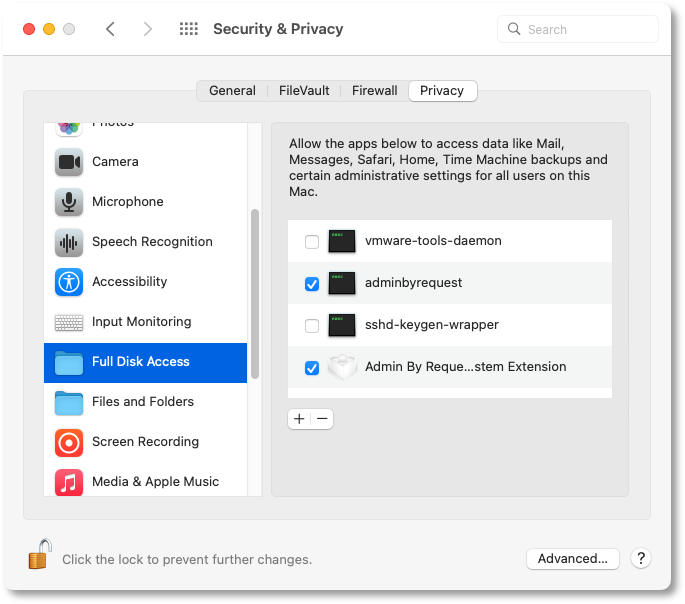
On your Mac device, navigate to System Preferences > Security & Privacy > Privacy tab and select Full Disk Access from the list. You’ll need to supply your password to unlock and make changes.
-
Select both adminbyrequest and Admin By Request System Extension in the list of apps (i.e. ensure the boxes are checked):
-
Lock the tab to save changes and close the System Preferences window.
macOS 13 (Ventura) through macOS 26 (Tahoe)
-
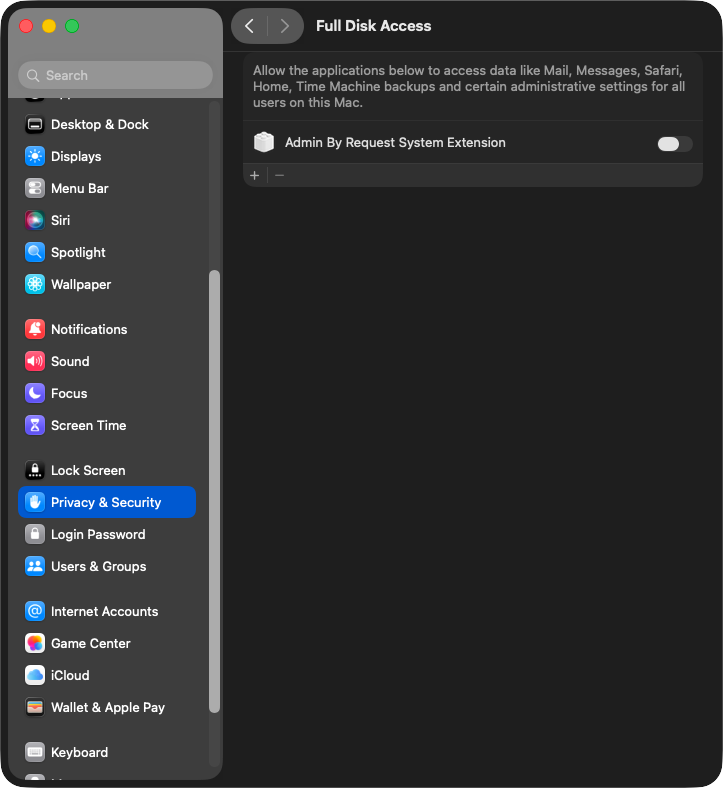
On your Mac device, navigate to System Settings > Privacy & Security tab and select Full Disk Access from the list. You’ll need to supply your password to unlock and make changes.
-
Enable the Admin By Request System Extension:
-
Drag and drop the adminbyrequest executable from Finder into the Full Disk Access list in System Settings. Note that this step is not required in macOS 26.3 or above.
That completes the requirements for enabling both the Endpoint Privilege Management and Secure Remote Access components of Admin By Request.
Using Jamf - FDA
Admin By Request provides a set of configuration files to assist with configuration in Jamf. Download the set here and visit Creating and Uploading PLIST or .mobileconfig File for instructions on deployment.
Alternatively, follow the procedure below if you wish to build your own Jamf Configuration Profiles to manage Mac endpoints:
-
In Jamf, go to Computers > Configuration Profiles.
-
Create a new profile and configure it as follows:
-
Name: give the profile a name that helps explain what application it is giving rights to. In this example, we use ABR - PPPC.
-
Category, select Applications.
-
Distribution Method, select Install Automatically.
-
Level, select Computer Level.
-
-
Navigate from the General tab to the Privacy Preferences Policy Control tab:
-
Identifier, enter /Library/adminbyrequest/adminbyrequest.
-
Identifier Type, select Path.
-
For Code Requirement, enter the following line of code:
Copyidentifier "com.fasttracksoftware.adminbyrequest" and anchor apple generic and certificate 1[field.1.2.840.113635.100.6.2.6] /* exists */ and certificate leaf[field.1.2.840.113635.100.6.1.13] /* exists */ and certificate leaf[subject.OU] = AU2ALARPUPIMPORTANTThe code snippet is all one line. Use the Copy button in the top right corner of the code box to copy the code to the clipboard.
-
Under App or Service, select SystemPolicyAllFiles and under Access, select Allow:
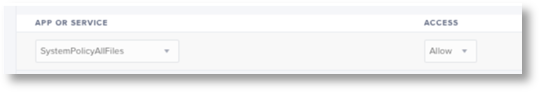
Under App or Service, select Accessibility and under Access, select Allow.
-
Save the profile.
-
-
Deploy and use this profile to enable FDA for all your macOS endpoints.
Using Intune - FDA
Similar to Jamf, Intune uses Configuration Profiles to manage Mac endpoints:
-
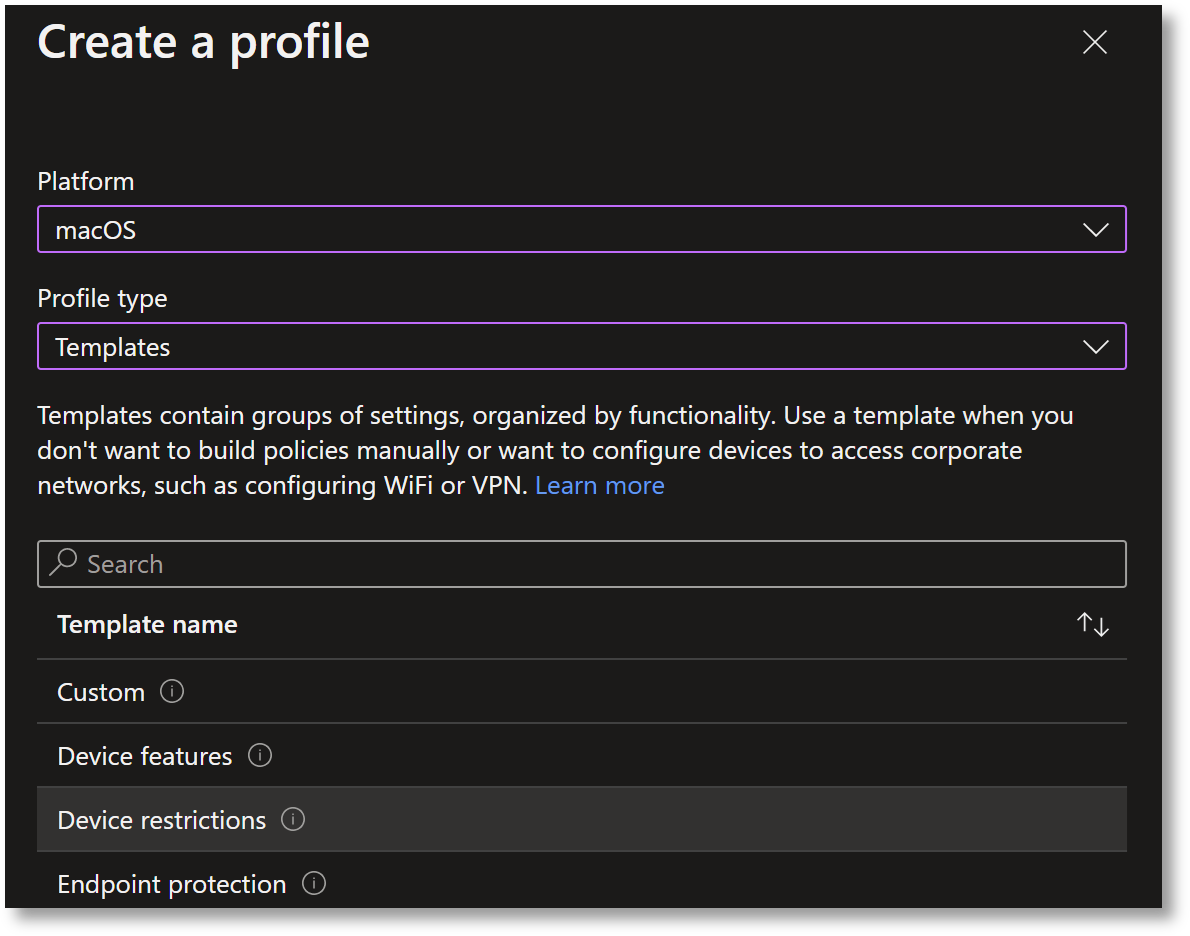
In Intune, under Configuration Profiles, select Create Profile.
-
Enter the following details into the Create a Profile form:
-
Platform: macOS
-
Profile type: Templates
-
Template name: ABR – FDA
-
-
Click Create.
-
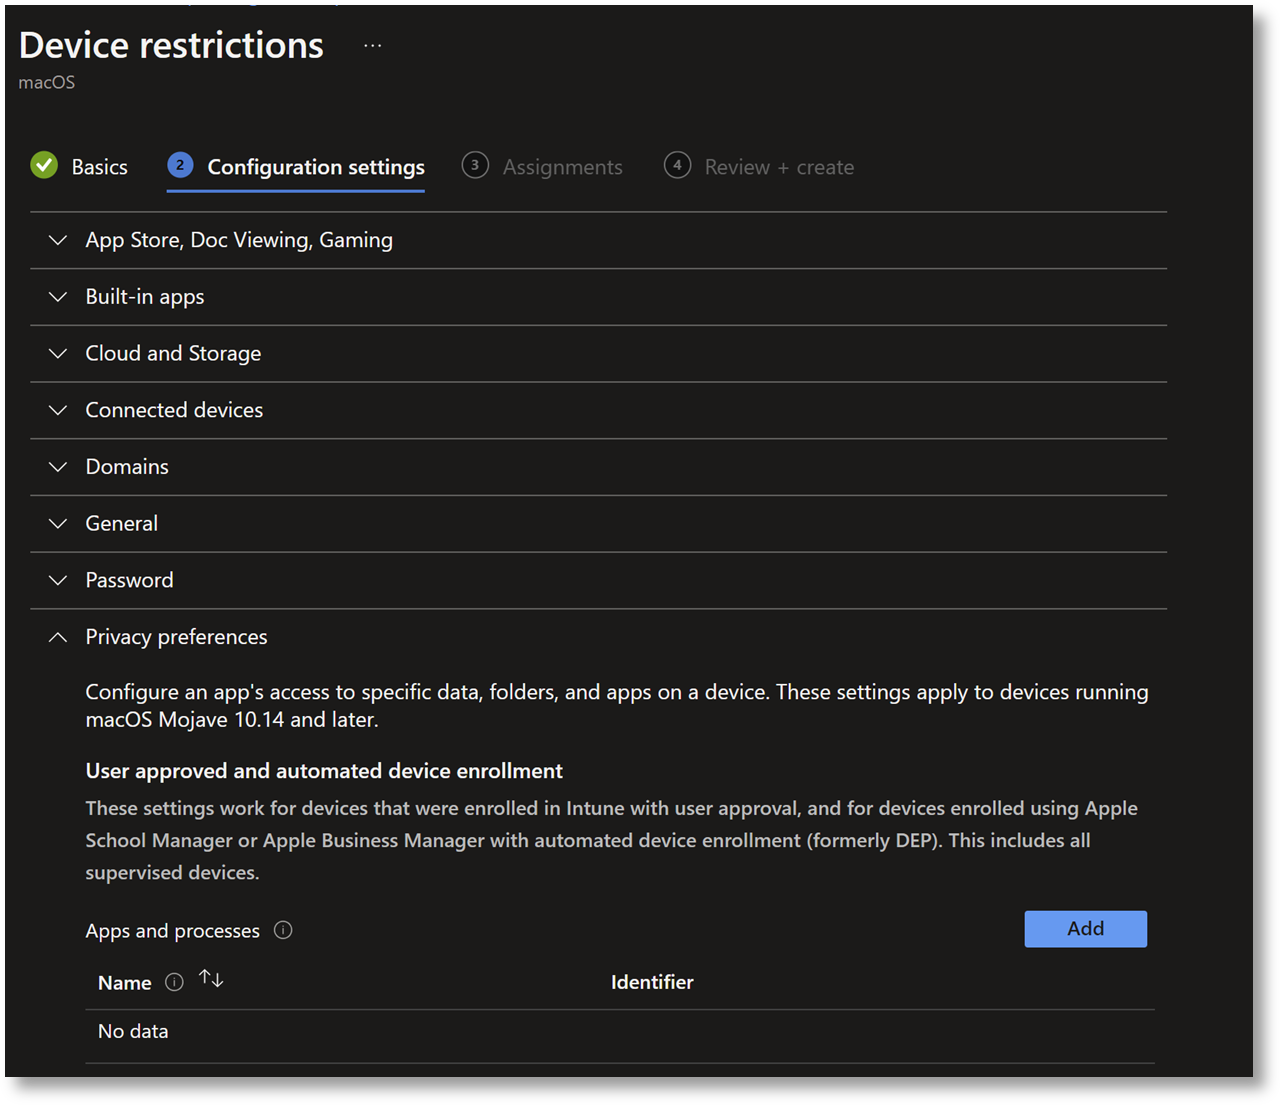
Under Device restrictions, go to Configuration settings.
-
Select Privacy preferences and click Add:
-
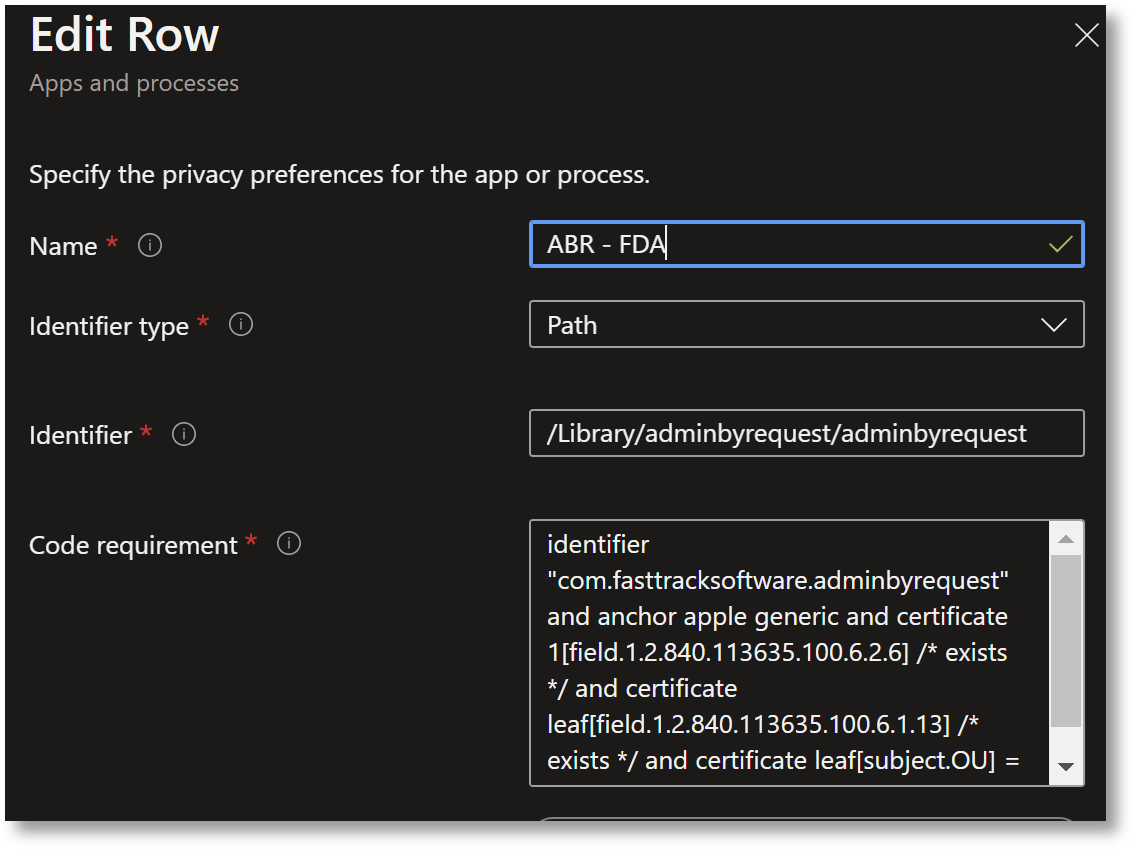
In the Edit Row form, enter the following:
-
Name: ABR – FDA
-
Identifier type: Path
-
Identifier: /Library/adminbyrequest/adminbyrequest
-
For Code Requirement, enter the following line of code:
Copyidentifier "com.fasttracksoftware.adminbyrequest" and anchor apple generic and certificate 1[field.1.2.840.113635.100.6.2.6] /* exists */ and certificate leaf[field.1.2.840.113635.100.6.1.13] /* exists */ and certificate leaf[subject.OU] = AU2ALARPUPIMPORTANTThe code snippet is all one line. Use the Copy button in the top right corner of the code box to copy the code to the clipboard.
-
-
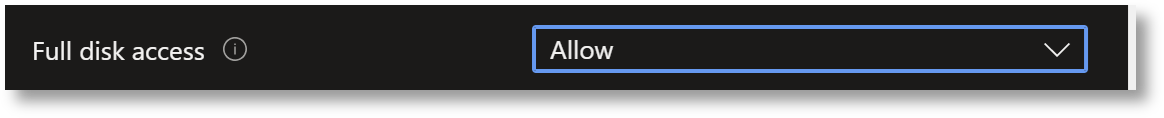
Finally, select Allow in field Full disk access:
The completed form: